Passkey-first
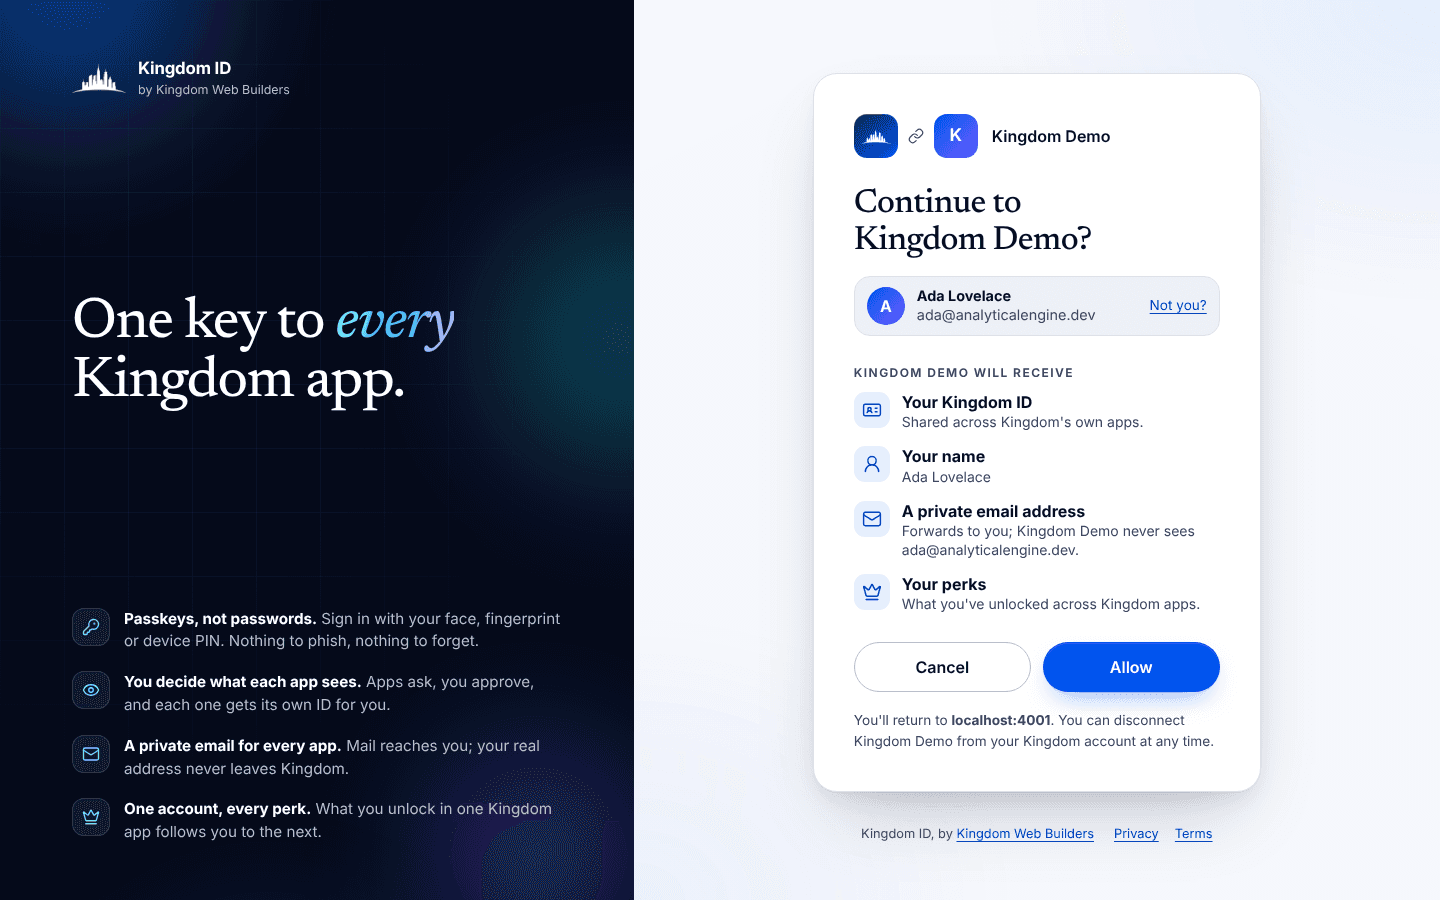
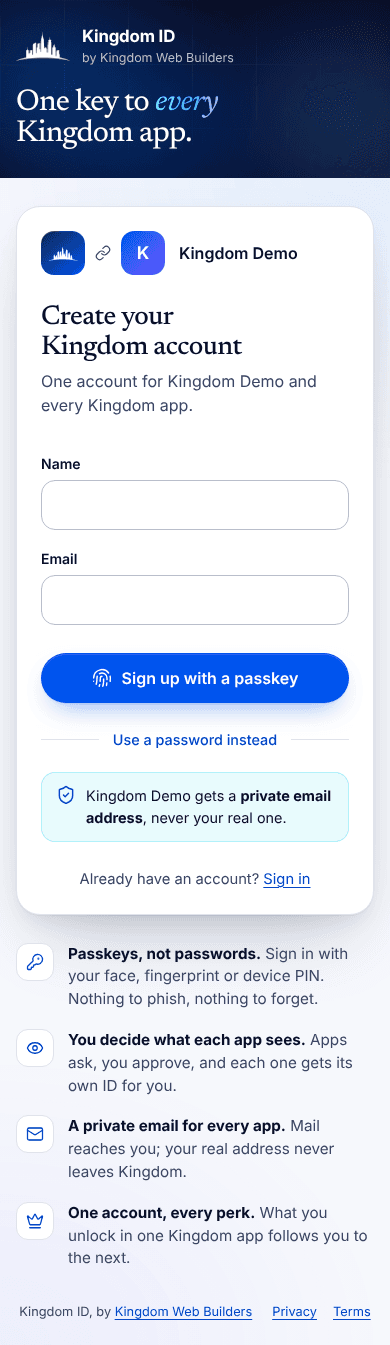
Sign in with a face, fingerprint or device PIN. Nothing to phish and nothing to forget. Passwords remain as a fallback, and an app can insist on a phishing-resistant sign-in.
Kingdom ID is the account system behind every app we build: one passkey sign-in for Cappuccino, InkSpirit and whatever comes next. It's a complete OAuth 2.0 and OpenID Connect provider we wrote directly from the specifications, with no OIDC library underneath.
24
specifications implemented
0
failures on the OpenID Foundation Basic OP plan
222
automated tests, browser and server
2.06×
throughput from a second instance
Sign in with a face, fingerprint or device PIN. Nothing to phish and nothing to forget. Passwords remain as a fallback, and an app can insist on a phishing-resistant sign-in.
Outside apps each get their own ID for a person, so they can't link anyone across apps. Kingdom's own apps share one, so perks and history follow the member.
Each app gets its own relay address. Mail reaches the member, replies go back out through the relay, and the real address never leaves Kingdom.
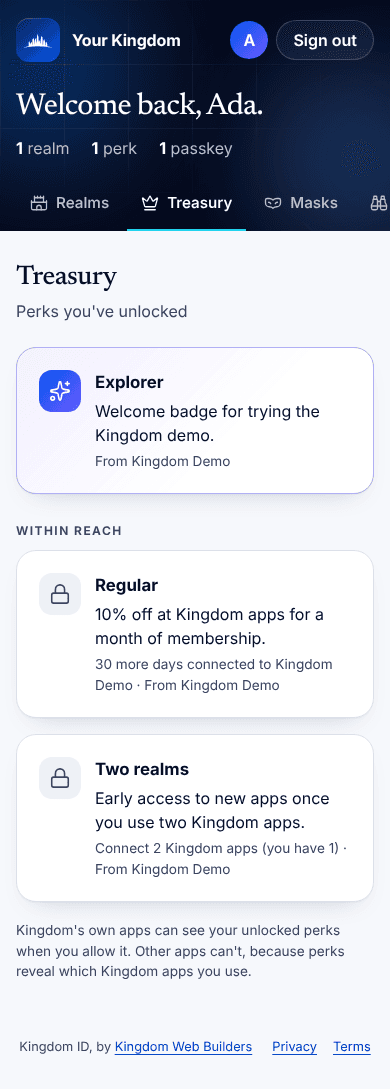
Your Kingdom shows every connected app, exactly what each one received, perks that carry across apps and a security timeline. One click disconnects an app everywhere.
Built with TypeScript, Node, Fastify, Postgres and Redis. Stateless, so any instance can serve any request.
Kingdom ID is the kind of system we build for clients: standards-based, secure from the first commit, and yours to own. If your products need one sign-in, or your sign-in needs to be trustworthy, let's talk.